Cyber Essentials Plus
In many sectors, Cyber Essentials Plus is the difference between being in the running to win new business, and not even being considered.
Failing is expensive and avoidable
Cyber Essentials Plus is not a paperwork exercise. Where the basic certification is self-assessed, Plus involves an independent assessor testing your environment directly, and the scheme has become steadily less forgiving.
Version 3.3 came into force in April 2026. Cloud services are now explicitly in scope and cannot be excluded. Multi-factor authentication carries auto-fail conditions. High-risk and critical updates, and anything with a CVSS score of 7 or above, must be applied within 14 days of release, and a single unpatched device found on assessment day is enough to fail the whole thing.
Where LIMA fits
The assessment itself is delivered by an accredited certification body, and we work with a preferred partner for that. It is the least interesting part of the process. Everything that decides the outcome happens beforehand.
Our approach
Review
A Cyber Resilience Assessment establishes where you stand against the current framework and exactly which controls you would fail on today.
Improve
We close the gaps. Patching runs through VDR to Cyber Essentials Plus SLAs, and configuration or architectural work is scoped and delivered as a project.
Validate
We review your submission before it is sent, so errors, gaps and anything likely to raise a question are sorted in advance.
Assess
On the day, we are available to the assessor for questions relating to the environment we manage, which for some of our customers means answering on their behalf.
Passing first time, then staying passed
We have taken customers large and small through this process, several of them repeatedly as the standard has changed. They usually pass first time and they hold certification year on year.
Renewal is where organisations tend to come unstuck. A build that satisfied Willow will not necessarily satisfy Danzell (the latest CE+ version) and the annual update means the target moves. Because we manage the environment, the controls that need to hold between assessments hold continuously rather than being reconstructed in the six weeks before renewal.
Trusted by
The VDR connection
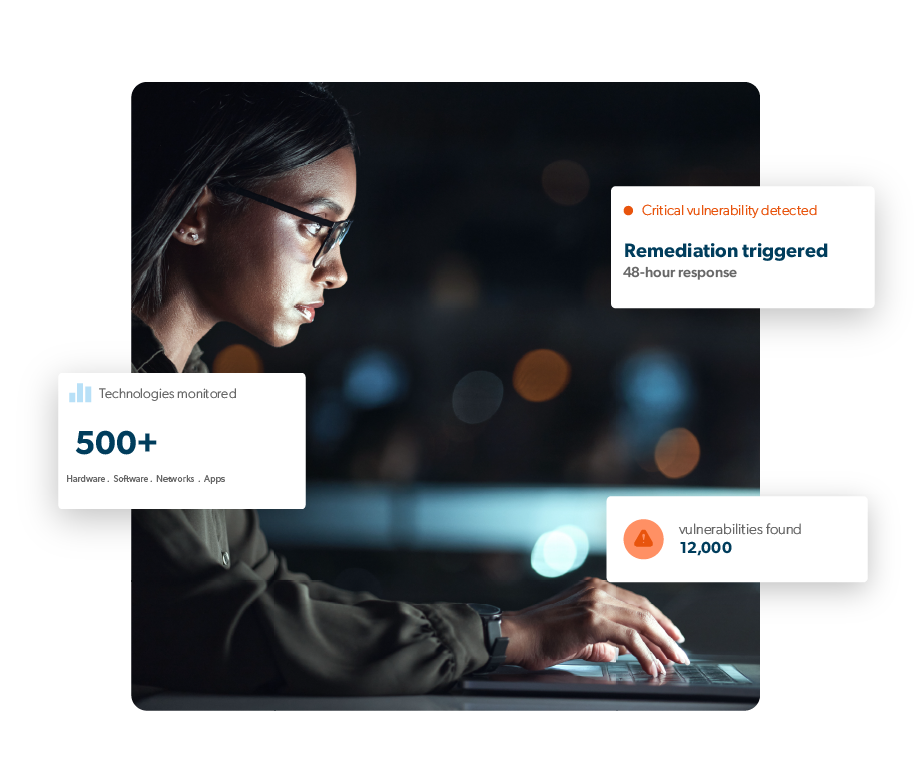
Security Update Management is the control that fails most organisations, and it is the one that requires continuous effort rather than a one-off fix. VDR remediates vulnerabilities across 500+ technologies with SLAs written to align with Cyber Essentials Plus requirements, which is why so many of our customers pick it up while preparing to certify and keep it long after.
Why choose LIMA for Cyber Essentials Plus
We treat certification as the outcome of a well-run environment rather than a project in its own right. That is why our customers pass, and why they pass again the following year without a huge headache.
See our latest customer stories